Zero-Trust BCDR Platform
Discover the technological foundation of StateWarden® that ensures your business continuity.
Unique Security Engine
Post-Quantum ML-KEM Encryption
StateWarden runs cascaded cryptography in production: AES-256-GCM combined with the standardized ML-KEM (FIPS 203) algorithm - post-quantum key establishment protecting every newly paired agent.
- Cascaded Cryptography: ML-KEM (FIPS 203) secures classical AES-256-GCM encryption against future quantum threats.
- Hardware Identity: Every node is authorized via unique X.509 mTLS certificates.
- Zero-Knowledge: Keys never leave your server - third parties have no technical access to your data.
// PrimeKEM Standard Payload
Audit Readiness
Legal Compliance and GDPR
We designed the system to automate the fulfillment of NIS2, DORA, and GDPR requirements for boards and DPOs.
- Geographic Isolation: Enforcing data storage location at the network routing level.
- Data Destruction: Cryptographic overwriting allows for the irreversible deletion of specific blocks.
- Audit Trails: A system log recording changes to security policy configuration.
Transfer Optimization
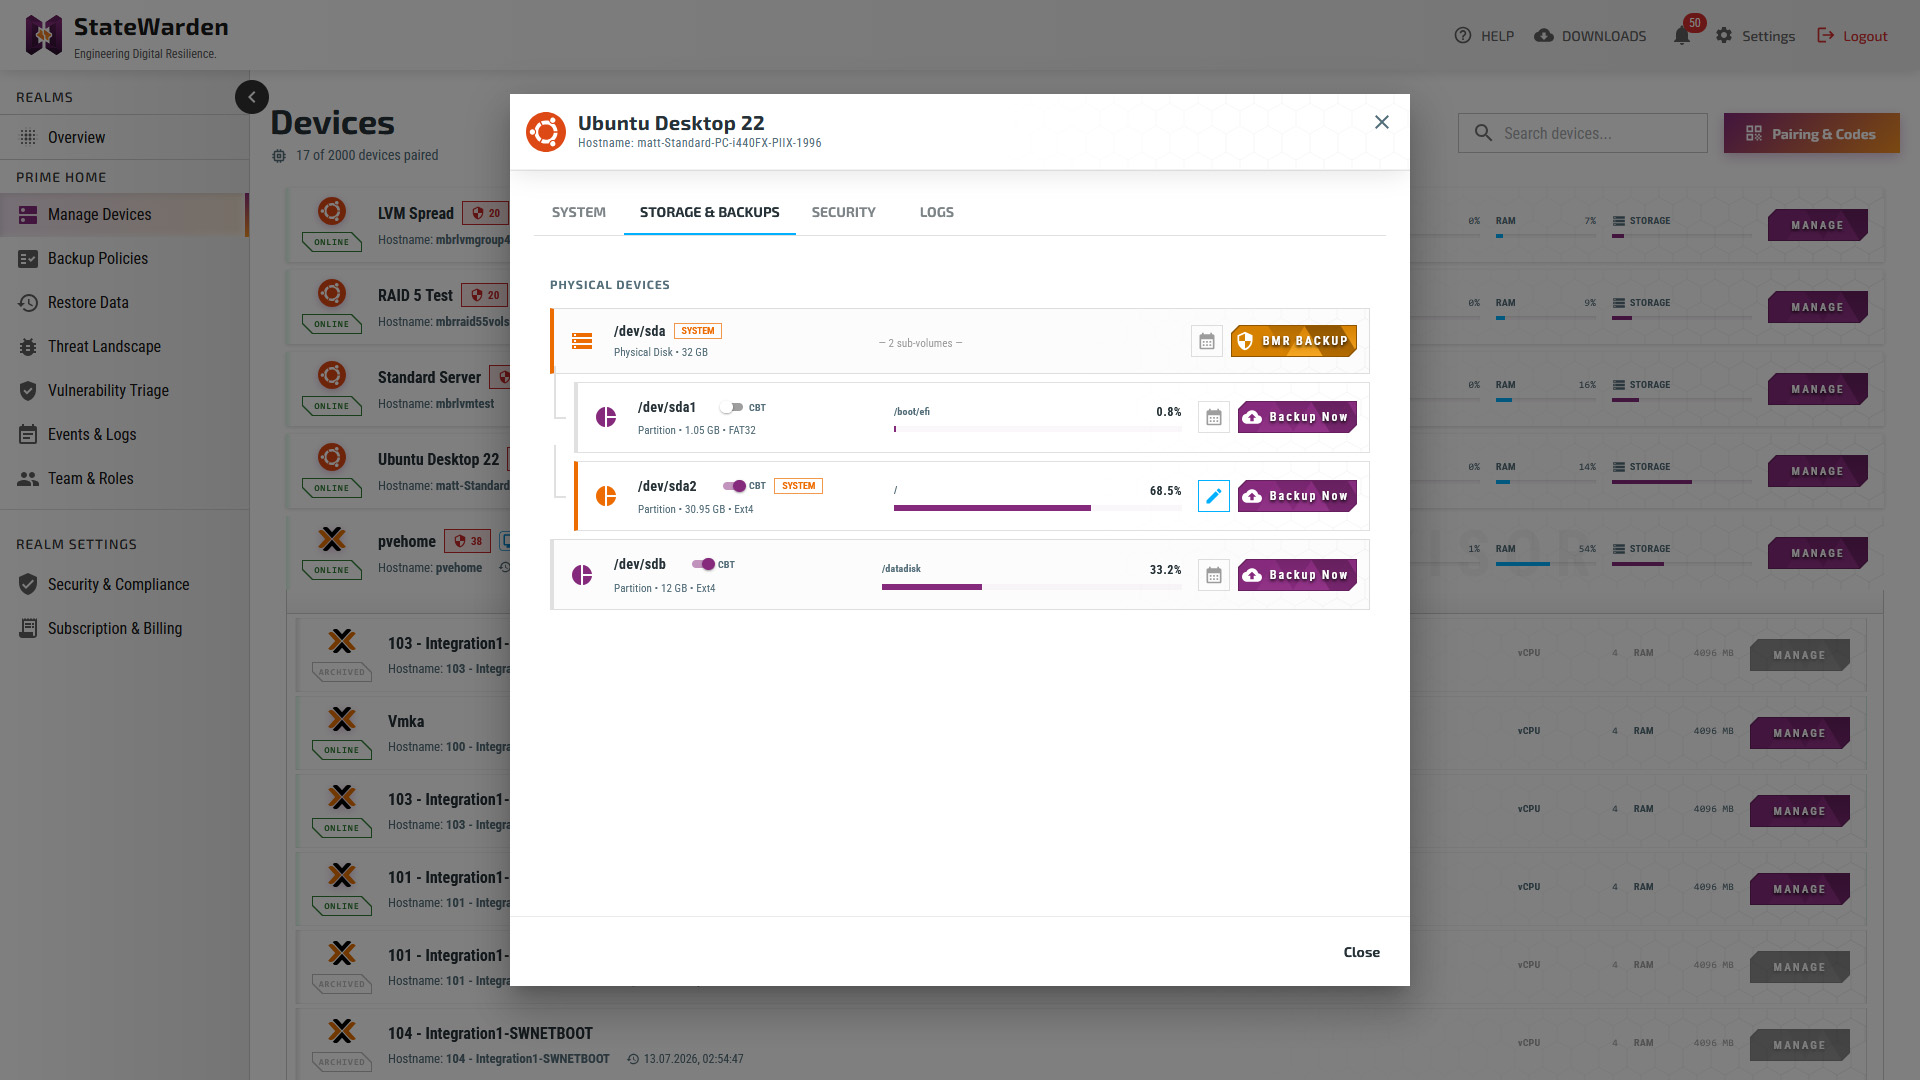
Change Block Tracking (CBT)
We transmit only what has changed. Change Block Tracking technology drastically shortens backup times and reduces network load.
- Linux: Integration with Device Mapper (dm-era) mechanisms.
- Windows: Utilization of native Volume Shadow Copy Service (VSS) services.
- Deduplication: Filtering duplicates before transfer in a client-side architecture.
Operational Capabilities
A summary of functions safeguarding business continuity.
WORM Storage
The data vault operates as an append-only monolith: the vault copy cannot be encrypted or overwritten by ransomware running on the protected host. Vigil scans backup content against 200,000+ known vulnerabilities and malware signatures - before you restore, not after.
Block Mapping (NBD)
Instant operational recovery via block-level mapping. Before a backup is mounted, Vigil scans backup content against 200,000+ known vulnerabilities and malware signatures - before you restore, not after.
Metrics Collection
The agent collects and transmits resource utilization metrics (CPU, RAM, Disk I/O) from individual managed nodes.
Vulnerability Verification (Vigil)
Automated infrastructure monitoring. We correlate collected data with global CVE databases (NVD, OSV), informing about vulnerabilities in real time.
Secure Management Channels
Manage the entire network through secure, audited channels without the need to configure dedicated VPN tunnels or open ports.
Client-Side Deduplication
Optimized storage via client-side deduplication and encryption at the source. Vigil scans backup content against 200,000+ known vulnerabilities and malware signatures - before you restore, not after.
EU Sovereignty &
The solution is subject to European legislation. Backup data is processed under EU jurisdiction, outside the reach of the US CLOUD Act.
Efficiency
Our software is a single, optimized file with a measured near-zero idle footprint (0.02% CPU, ~24 MB RAM)
Uncompromising Quality Control
StateWarden's architecture undergoes rigorous security and performance audits. We develop software in a "Zero-Defect" spirit, with a total focus on the stability of Mission-Critical environments.